

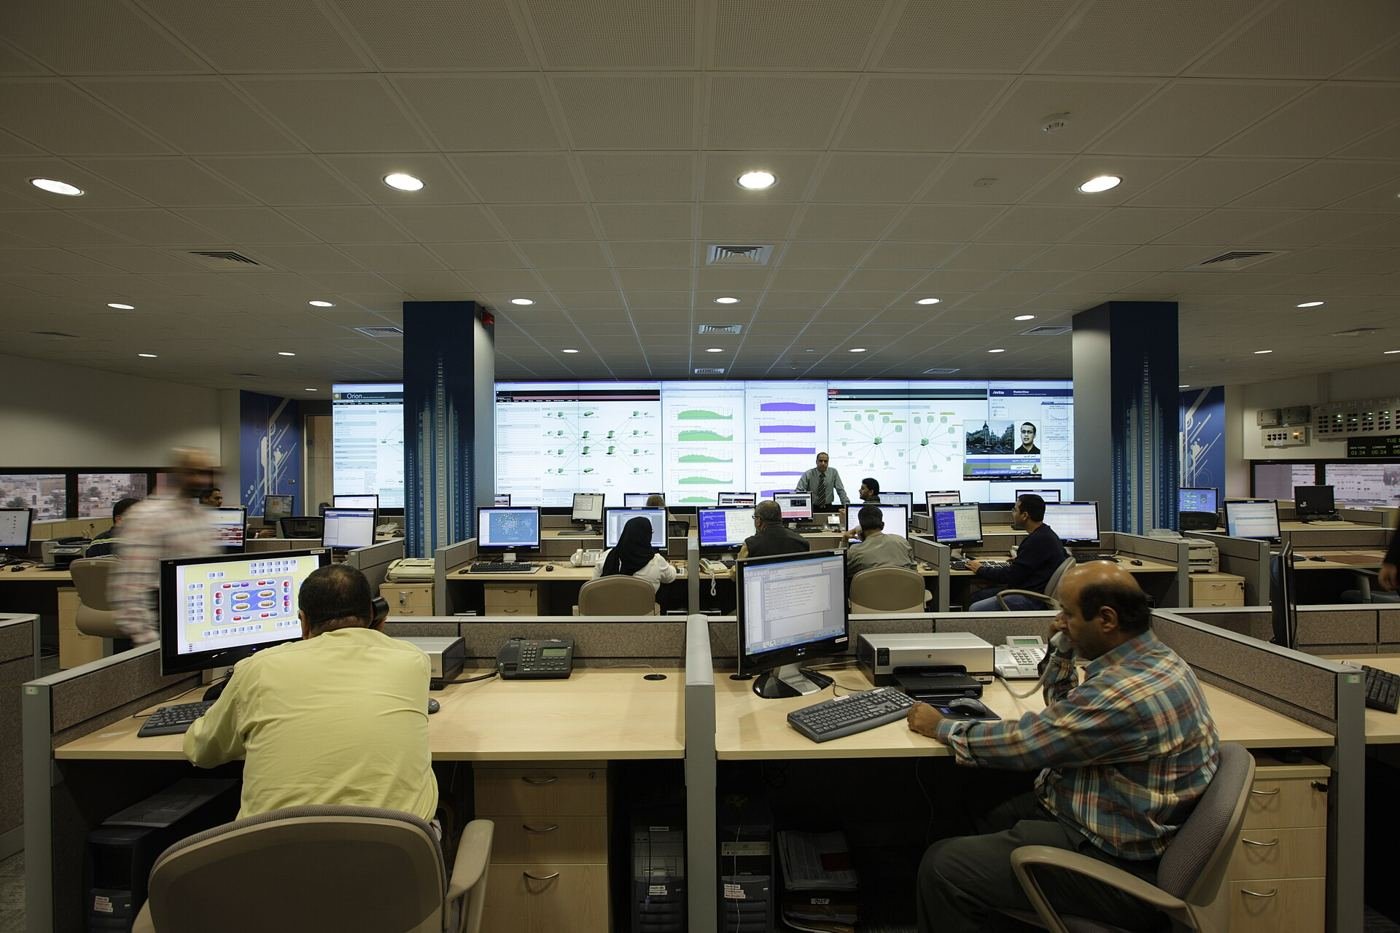
Cyber security operations centres are tracking a fresh wave of ransomware groups that target hospitals, schools and local councils through stolen staff passwords. Analysts watch network traffic around the clock, correlating alerts from many systems to separate genuine attacks from harmless noise quickly. Faster detection matters because containing an infected machine early can prevent criminals spreading across an entire organisation within just a few hours today.
What the Evidence Shows
Security leaders advise organisations to patch systems promptly, back up critical data offline and rehearse response plans before a real incident tests them. Multi factor authentication and strict access limits make stolen passwords far less useful, reducing the damage attackers can cause after entry. Regular staff training also helps employees spot suspicious messages and report them quickly, turning the whole workforce into an early warning system. Reporting and analysis from sources such as MIT Technology Review track the same developments, and specialists following ransomware threat monitoring centres say the direction is now consistent across independent lines of evidence.
The Wider Context
The wider context is an industry learning to ship capability and restraint together. Products built around ransomware threat monitoring centres now launch with safety evaluations, usage data and rollback plans as standard, because enterprise buyers and regulators ask for them in the first meeting. Companies that treated those questions as friction are discovering they have become the purchase criteria.
What Happens Next
What happens next for ransomware threat monitoring centres depends less on another breakthrough than on the unglamorous work of reliability, pricing and support. The buyers evaluating it now are not enthusiasts; they are operators with budgets and auditors, and their checklists will decide the timeline. On the evidence of the current pilots, the technology has earned the right to be judged by them. You can follow related developments in our coverage of technology.
There is a practical lesson in all of this for readers deciding what to do today. Start with the verified facts, be wary of anyone promising certainty, and prefer reversible steps while the evidence is still developing. Circumstances differ by country, income and personal situation, so general guidance should always be weighed against your own context before you act on it in any significant or lasting way.
It is also worth remembering how quickly the picture in this area has changed before. Positions that looked settled a few years ago have been revised as new data arrived, and the same humility is appropriate now. The strongest coverage of this subject, and the most useful advice, tends to come from sources that update their views openly when the facts move, rather than defending an earlier position long after it has stopped fitting the evidence available.
None of this will be settled by a single announcement, study or product launch. The pattern to watch is accumulation: independent confirmations, honest reporting of failures and steady improvement in the underlying numbers. Readers who follow those signals, rather than the loudest claim of the week, will understand this subject better than most of the commentary surrounding it suggests is possible.
