


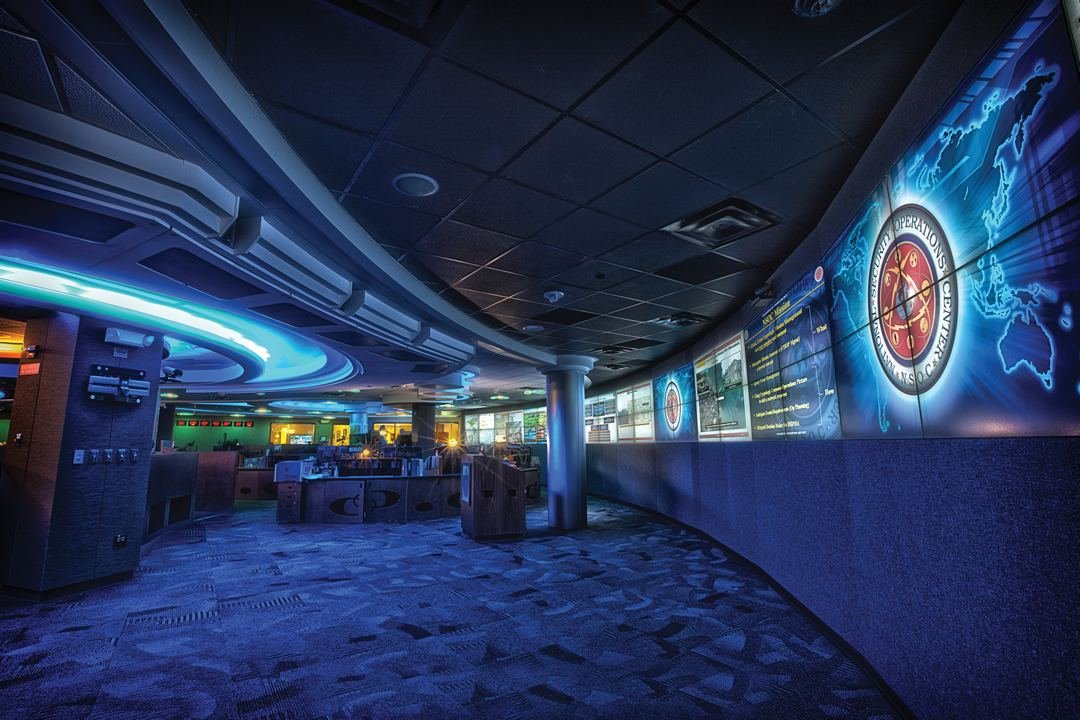
Security teams are using faster detection tools to contain modern breaches before stolen data, locked systems or disrupted services can spread across an organisation. Operations centres now monitor networks around the clock, combining automated alerts with analysts who investigate unusual behaviour and decide when a threat is real. The aim is to shorten the time between intrusion and response, because every minute can increase recovery costs and damage trust with customers and partners. Attackers increasingly use stolen passwords, phishing messages and unpatched software, so basic controls remain essential alongside newer monitoring platforms and intelligence feeds for teams. Leaders say clear incident plans, tested backups and honest communication help organisations recover faster when prevention alone cannot stop every attempted attack.
What the Evidence Shows
Analysts in a security operations centre review alerts by risk, checking whether a login, file transfer or system change fits normal patterns for users. Automation helps filter routine noise, but human judgement remains vital when attackers imitate trusted accounts or move slowly to avoid raising obvious alarms. Regular patching, multifactor authentication and limited admin access reduce the paths available to intruders, while staff training helps people spot suspicious requests more quickly. Organisations are also rehearsing response steps, ensuring legal, technical and communications teams understand their roles before a real incident creates pressure and confusion. Strong detection is therefore not a single product, but a coordinated practice built on visibility, preparation, skilled people and rapid decisions. Reporting and analysis from sources such as MIT Technology Review track the same developments, and specialists following faster detection to contain breaches say the direction is now consistent across independent lines of evidence.
The Wider Context
The wider context is an industry learning to ship capability and restraint together. Products built around faster detection to contain breaches now launch with safety evaluations, usage data and rollback plans as standard, because enterprise buyers and regulators ask for them in the first meeting. Companies that treated those questions as friction are discovering they have become the purchase criteria.
What Happens Next
What happens next for faster detection to contain breaches depends less on another breakthrough than on the unglamorous work of reliability, pricing and support. The buyers evaluating it now are not enthusiasts; they are operators with budgets and auditors, and their checklists will decide the timeline. On the evidence of the current pilots, the technology has earned the right to be judged by them. You can follow related developments in our coverage of technology.
There is a practical lesson in all of this for readers deciding what to do today. Start with the verified facts, be wary of anyone promising certainty, and prefer reversible steps while the evidence is still developing. Circumstances differ by country, income and personal situation, so general guidance should always be weighed against your own context before you act on it in any significant or lasting way.
