

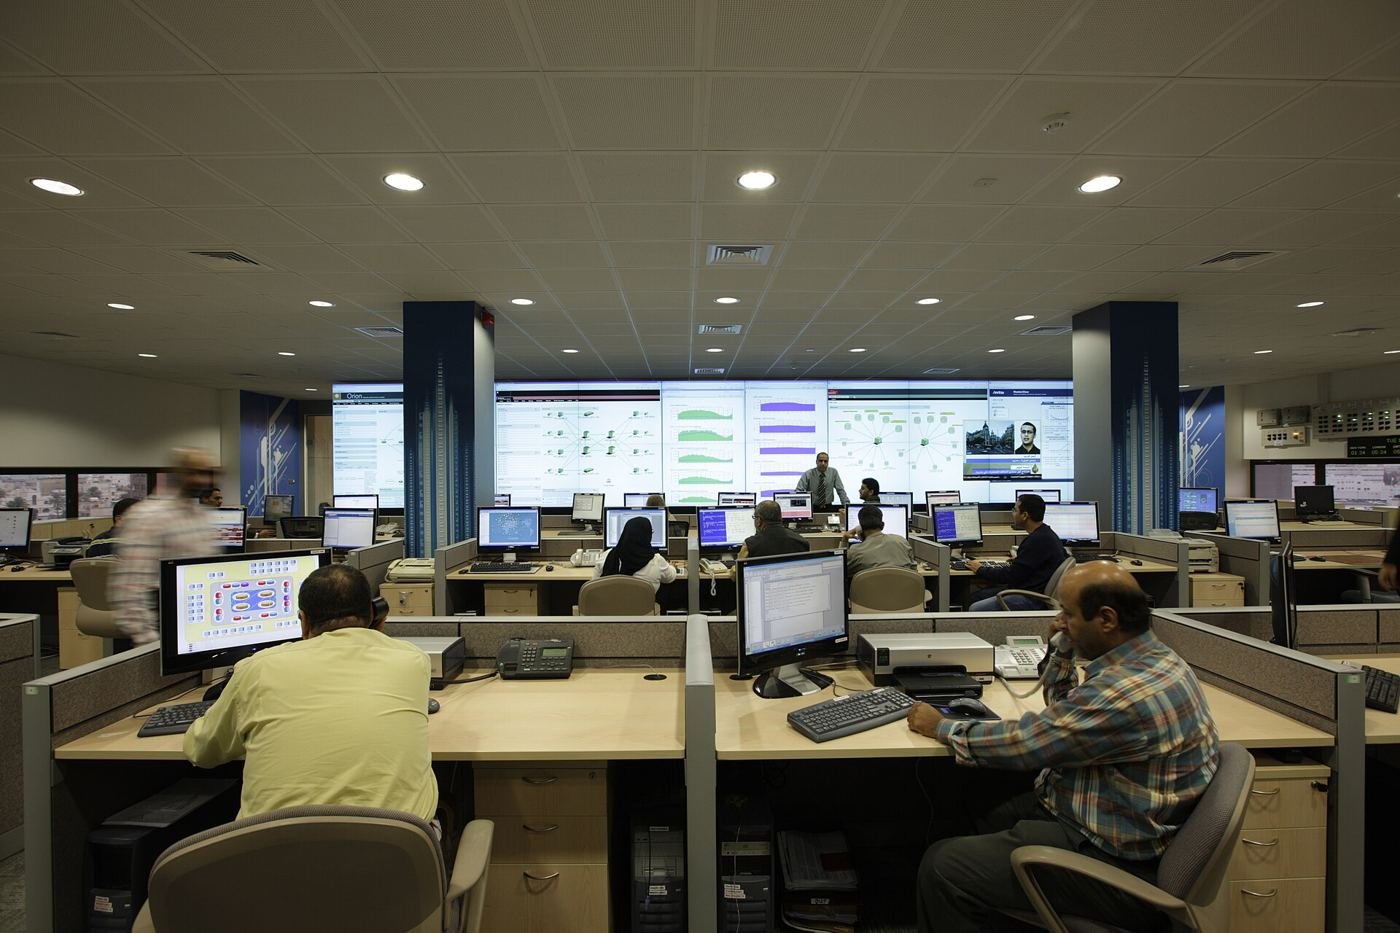
A busy security team may receive thousands of automated alerts in a single day, far more than any group of analysts could investigate one by one with equal care and attention. Triage is the disciplined process that sorts this flood, deciding within moments which warnings suggest a genuine attack, which reflect harmless everyday activity and which can safely wait for a quieter hour. The challenge is known as alert fatigue, and it is dangerous precisely because a real intrusion can hide inside the noise of routine warnings until nobody notices it in time. Analysts begin by enriching each alert with context, such as whether the account involved normally behaves this way, whether the device is patched and whether similar events are appearing across the organisation simultaneously. Automation handles the obvious cases, closing alerts that match known safe patterns and grouping duplicates so that one incident is not counted fifty separate times by mistake. Severity scores combine the sensitivity of the affected system with the confidence of the detection, pushing a possible attack on a finance server ahead of a minor warning from a test machine. Done well, triage protects human attention for the judgement calls that machines still make badly.
What the Evidence Shows
Experience shapes triage as much as tooling, because a seasoned analyst develops instincts for the odd detail that separates an attacker quietly exploring from an employee simply working in an unusual way. Teams refine their rules constantly, tuning out alerts that repeatedly prove harmless while lowering thresholds where a missed detection would carry unacceptable consequences for customers or regulators. False positives are not merely annoying, since every wasted investigation consumes the limited hours available for threat hunting, training and improving the defences that generate fewer alerts in the first place. Modern platforms increasingly use machine learning to rank alerts by similarity to past confirmed incidents, although analysts remain responsible for checking that the model has not quietly learned the wrong lessons. Clear escalation paths matter during serious incidents, ensuring that a worrying alert found at three in the morning reaches decision makers quickly instead of waiting in a queue until office hours. Metrics such as time to acknowledge and time to contain show whether triage is improving or slowly drowning under growing volumes of connected devices and cloud services. The goal is not zero alerts, but a queue small and honest enough that every genuine threat gets noticed. Reporting and analysis from sources such as MIT Technology Review track the same developments, and specialists following how analysts triage security alerts say the direction is now consistent across independent lines of evidence.
The Wider Context
The wider context is an industry learning to ship capability and restraint together. Products built around how analysts triage security alerts now launch with safety evaluations, usage data and rollback plans as standard, because enterprise buyers and regulators ask for them in the first meeting. Companies that treated those questions as friction are discovering they have become the purchase criteria.
What Happens Next
What happens next for how analysts triage security alerts depends less on another breakthrough than on the unglamorous work of reliability, pricing and support. The buyers evaluating it now are not enthusiasts; they are operators with budgets and auditors, and their checklists will decide the timeline. On the evidence of the current pilots, the technology has earned the right to be judged by them. You can follow related developments in our coverage of technology.
There is a practical lesson in all of this for readers deciding what to do today. Start with the verified facts, be wary of anyone promising certainty, and prefer reversible steps while the evidence is still developing. Circumstances differ by country, income and personal situation, so general guidance should always be weighed against your own context before you act on it in any significant or lasting way.
