


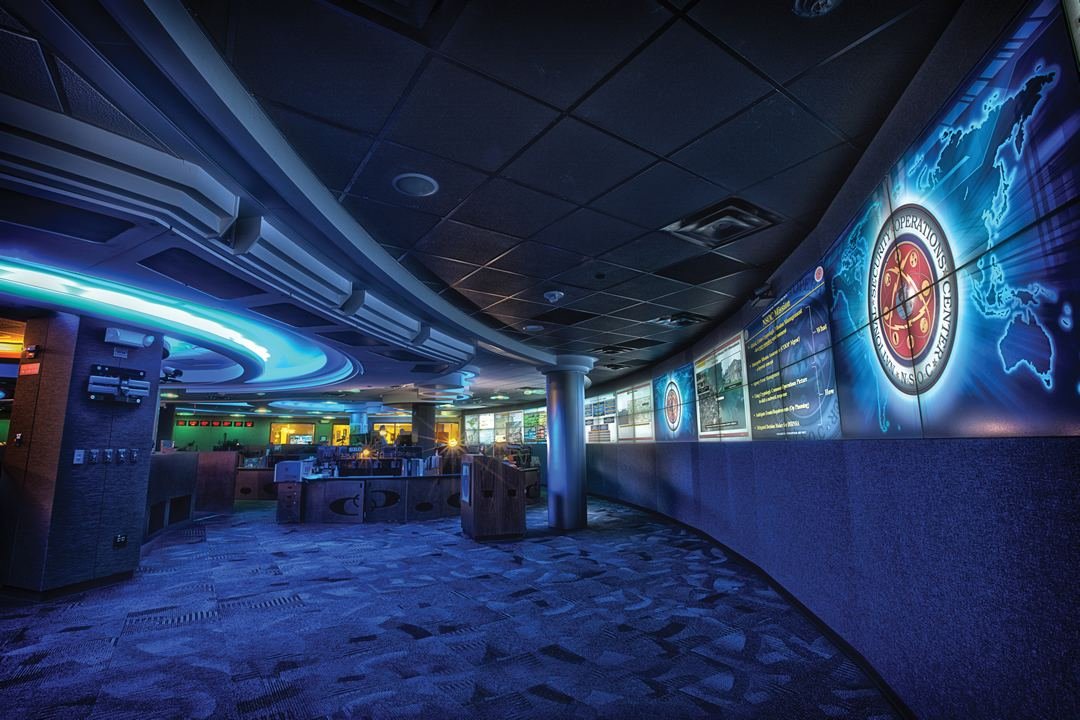
Security operations centres watch networks around the clock, giving organisations a dedicated team and workspace for spotting suspicious activity before it turns into a damaging incident. Analysts follow alerts from firewalls, laptops, servers and cloud services, piecing together whether an unusual sign in, a strange file or a sudden surge in traffic is harmless behaviour or the first sign of an attack. The work is less dramatic than films suggest, because most shifts involve patient checking, careful notes and quick conversations that confirm whether a user really did log in from an unexpected place at an unusual hour. Automation helps by grouping related alerts and highlighting the events most likely to matter, yet human judgement remains essential when attackers deliberately imitate normal business activity to hide in plain sight. Centres also coordinate the response when something serious is confirmed, isolating affected machines, preserving evidence and helping leaders decide what to tell staff, customers and regulators in the right order. For hospitals, councils, banks and growing companies, that calm coordination can shorten disruption and protect trust when an incident becomes public knowledge.
What the Evidence Shows
Building an effective centre starts with knowing which systems matter most, what normal activity looks like and who has authority to act quickly outside office hours. Smaller organisations may share a managed service rather than employing a full overnight team, but responsibilities, response times and reporting must still be agreed clearly in advance. Regular practice exercises reveal weak points in contact lists, access controls and backup plans before a real attacker exposes them under pressure. Analysts need rest, training and manageable alert volumes, because tired people miss patterns and noisy tools quickly teach teams to ignore warnings altogether. Good centres review every incident afterwards, turning mistakes and near misses into better rules rather than blame for individuals on duty. Strong monitoring does not promise that attacks will never succeed, but it greatly improves the chance of catching them early and recovering in an orderly way. That preparation is what turns a frightening alert into a managed incident with a clear ending. Reporting and analysis from sources such as IEEE Spectrum track the same developments, and specialists following security operations centres network monitoring say the direction is now consistent across independent lines of evidence.
The Wider Context
Adoption of security operations centres network monitoring follows a familiar pattern with an unfamiliar speed. Early users tolerate rough edges in exchange for advantage, mainstream users arrive when the tool disappears into existing workflows, and the market consolidates around whoever made that transition feel effortless. Vendors are racing less on raw performance now than on integration, support and trust.
What Happens Next
The realistic forecast for security operations centres network monitoring is steady integration rather than sudden replacement: embedded in products people already use, improving in increments, and regulated in proportion to its reach. The companies and institutions that plan on that basis, training staff and redesigning processes instead of chasing launches, are the ones the adoption data tends to vindicate. You can follow related developments in our coverage of technology.
It is also worth remembering how quickly the picture in this area has changed before. Positions that looked settled a few years ago have been revised as new data arrived, and the same humility is appropriate now. The strongest coverage of this subject, and the most useful advice, tends to come from sources that update their views openly when the facts move, rather than defending an earlier position long after it has stopped fitting the evidence available.
